
You learn what your controls miss
Which step alerted, which was logged and never actioned, and which was invisible. That list is the deliverable, and no scan produces it.
Prove it. Do not assume it.
Objective-based Red Team engagements run from Dubai. We go after a crown jewel you name, the way a real intruder would, then show you exactly what your detection and response did about it.
Red Team engagements / year
VAPT engagements / year
CVE numbers assigned
Responsible disclosures
Company certifications
Red Teaming is an objective-based security engagement in which a team of operators attempts to reach a specific, named asset inside your organisation using the same methods a real intruder would, while your defenders are not told it is happening. It measures whether an attack would be detected and stopped, rather than how many vulnerabilities exist.
It is rarely the right first purchase. Run against an estate with nothing watching, it produces an expensive report confirming what you already suspected, which is why we say so before quoting, not after.
What an engagement is actually for, stated as outcomes you can hold us to, not as features.
Which step alerted, which was logged and never actioned, and which was invisible. That list is the deliverable, and no scan produces it.
An attack path graph showing how one ordinary foothold became access to the thing that matters. The order of the steps is the finding.
The purple debrief turns every step we took into detection content your own team writes and owns, in your own tooling.
Scope rationale, authorisation, findings with owners, remediation record and retest. That chain is what CBUAE, DESC, IAS and ADHICS examiners actually read.
Your incident process runs under conditions close to a genuine event, at a time when the consequences of it going badly are zero.
Every technique mapped to MITRE ATT&CK, so this engagement is comparable with the last one and with the next provider's.
In, through, out. Scroll an engagement from the first foothold to the report, and watch what your side of it does about each step.
A foothold, and a channel nobody is looking at.
A pretext your staff would plausibly accept opens one workstation. The beacon then calls home through github.com, because outbound traffic to a service your developers use all day is the last thing a proxy log flags.
The agent is not bypassed. It is switched off.
Credentials carry us sideways, then a signed but vulnerable driver goes in. From kernel space the EDR and XDR callbacks are simply unhooked. Where a path runs out, the client stands up a leg up for us, an Azure VM or a file share, so the engagement keeps testing rather than stalling.
A certificate is a better key than a password.
A SYSTEM token lifted out of the EPROCESS list gets us local privilege. Then AD CS does the rest: a template missing its security extension, mis-issued and mapped to a Domain Admin. No password was ever cracked.
One alert, and not the one you would expect.
The SOC catches an anomalous certificate request on the CA. Not the driver, not the token theft, not four hosts of lateral movement. Which step alerted, which was only logged, and how long we sat there is the actual finding.
Proof of access, never damage.
The evidence package leaves over the same covert channel it arrived on, which tests whether outbound movement is noticed at all. Nothing is encrypted, deleted or genuinely taken.
The engagement ends as detections, not a PDF.
The attack narrative, the path graph, and a detection gap analysis naming every step your controls did not see, turned into content your Blue Team owns at the purple debrief.
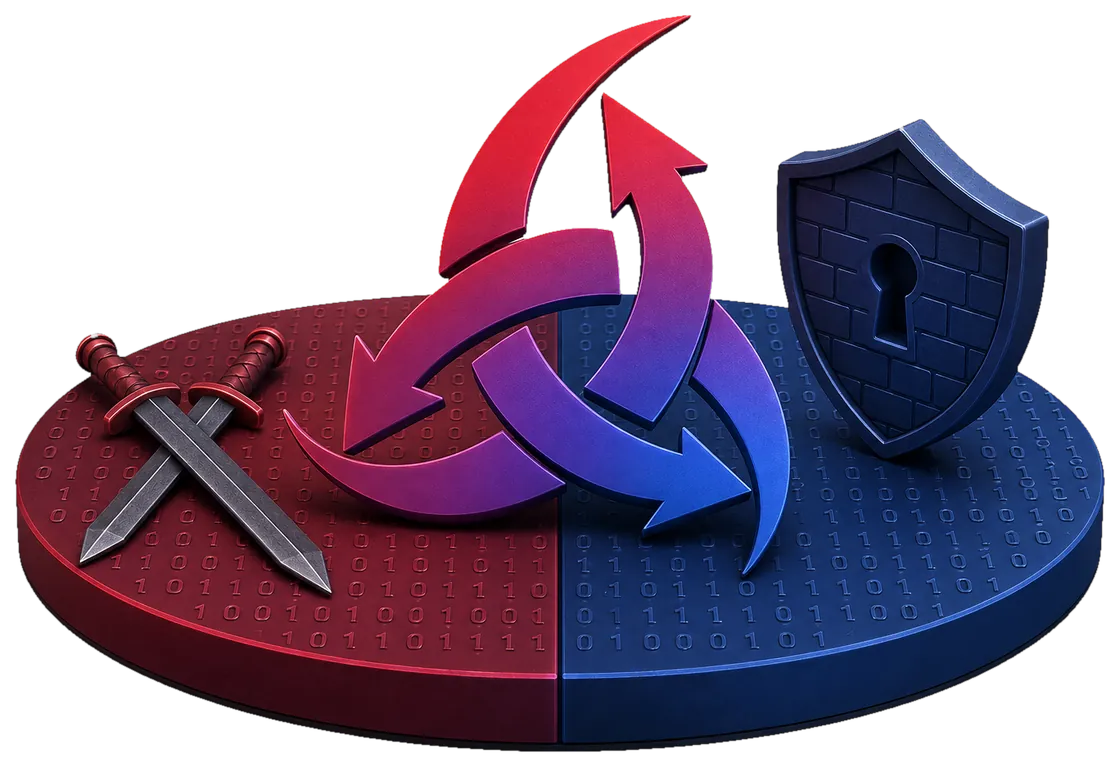
Two halves of the same question: one goes looking for the way in, the other has to see it coming. Run them together and you get the third.
Offence
Works against your estate the way a real intruder would, without warning anybody, to find out what actually happens rather than what is supposed to.
Offence and defence, together
The same attack run with the room watching. Nothing is hidden, so a gap becomes a working detection on the day it is found rather than in the report six weeks later.
Defence
Holds the estate every day: the detection content, the alerting and the response that has to work at three in the morning without anyone rehearsing it.
Three kinds of company sell this in the UAE and they are not interchangeable. This is where we actually sit, including where somebody else is the better answer.
| RTS | Regional VAPT firm | Global consultancy | |
|---|---|---|---|
| Who runs your engagement | Named operators who cleared a published bar | Often unnamed, frequently subcontracted | Named partner, delivery by junior staff |
| Operator standard published | Yes, four conditions, in writing | Rarely | Rarely at operator level |
| Objective-based scoping | Always. A named crown jewel or we do not call it Red Teaming | Usually asset-list based | Yes, at a price |
| Detection and response measured | Primary deliverable | Rarely, Blue Team is usually told | Yes |
| Purple debrief included | Included in the engagement | Sold separately if at all | Sold separately |
| Retest | Priced at scoping | Sold after the report | Sold after the report |
| UAE regulator mapping | CBUAE, DESC, IAS, ADHICS, all four | Usually one, named in passing | Generic, mapped to global frameworks |
| Evidence handling published | Yes, retention and destruction stated | Rarely | Contractual, not public |
| Time zone and travel | Dubai based, on site when useful | Regional | Often flown in, billed accordingly |
| Better choice than us when | Not applicable | You need high-volume routine scanning at low cost | You need a global multi-region programme with one contract |
The last row is deliberate. If you need cheap recurring scanning across two hundred assets, or a single contract covering eleven countries, we are not the right supplier and we would rather say so at this stage than at the third meeting.
Two supervisory programmes and one taxonomy. Knowing which is which is the fastest way to check a proposal.
ISO 27001
Information security management, certified at the company level.
ISO 9001
Quality management, which is what keeps engagement delivery repeatable.
You get an attack narrative in plain language, an attack path graph, a detection gap analysis that names which step your controls missed, and technical findings with remediation your team can act on directly.
Every technique is mapped to MITRE ATT&CK, so the report lines up with the framework your risk function already reports against. A retest is available once fixes land.
Most engagements here start because something external asked for one. Each of these is explained in full, with what it requires and how often.
RedTeam Security is operated by WebSec FZCO from IFZA Business Park in Dubai Silicon Oasis. That is where the company is registered and where the team sits. It is not the edge of where the work goes. Engagements run remotely or on site across the UAE and the wider GCC, into Europe, and into the United States, on the working week your organisation actually keeps.
Being based here is an advantage rather than a limit. The regulators, the sectors and the supplier ecosystems that shape an attack path in this region are not the ones a foreign provider will model by default. Where an engagement sits in Europe or North America, the same team and the same methodology travel to it.
Six to ten weeks end to end, covering scoping and rules of engagement, threat intelligence, the active phase, reporting and the debrief. Assumed breach is shorter because it skips initial access.
No. That is what makes the result meaningful. A small white team on your side holds the authorization letter and a deconfliction channel, so a real incident can be told apart from us within minutes.
Quoted per engagement, because scope, objective and estate size drive the effort. Tell us the crown jewel and roughly how large the estate around it is and we can put a number against it.
Nothing is encrypted, deleted or exfiltrated for real, and production changes are agreed in advance or not made. Every artefact we leave is listed for removal at clean closure.
Tell us the objective you want tested. We reply with a scope, a timeline and a quote.
The map loads only with your consent
It is an embed from Google Maps, and Google may set its own cookies when it loads, so it waits for the same choice as analytics.
IFZA Business Park, Building A2
Nadd Hessa, Dubai Silicon Oasis
Dubai, United Arab Emirates